
What is KubeOsprey?
KubeOsprey is a lightweight, open-source Kubernetes workspace for platform teams. It brings multi-cluster operations, observability, access control, and AI-assisted troubleshooting into one interface.
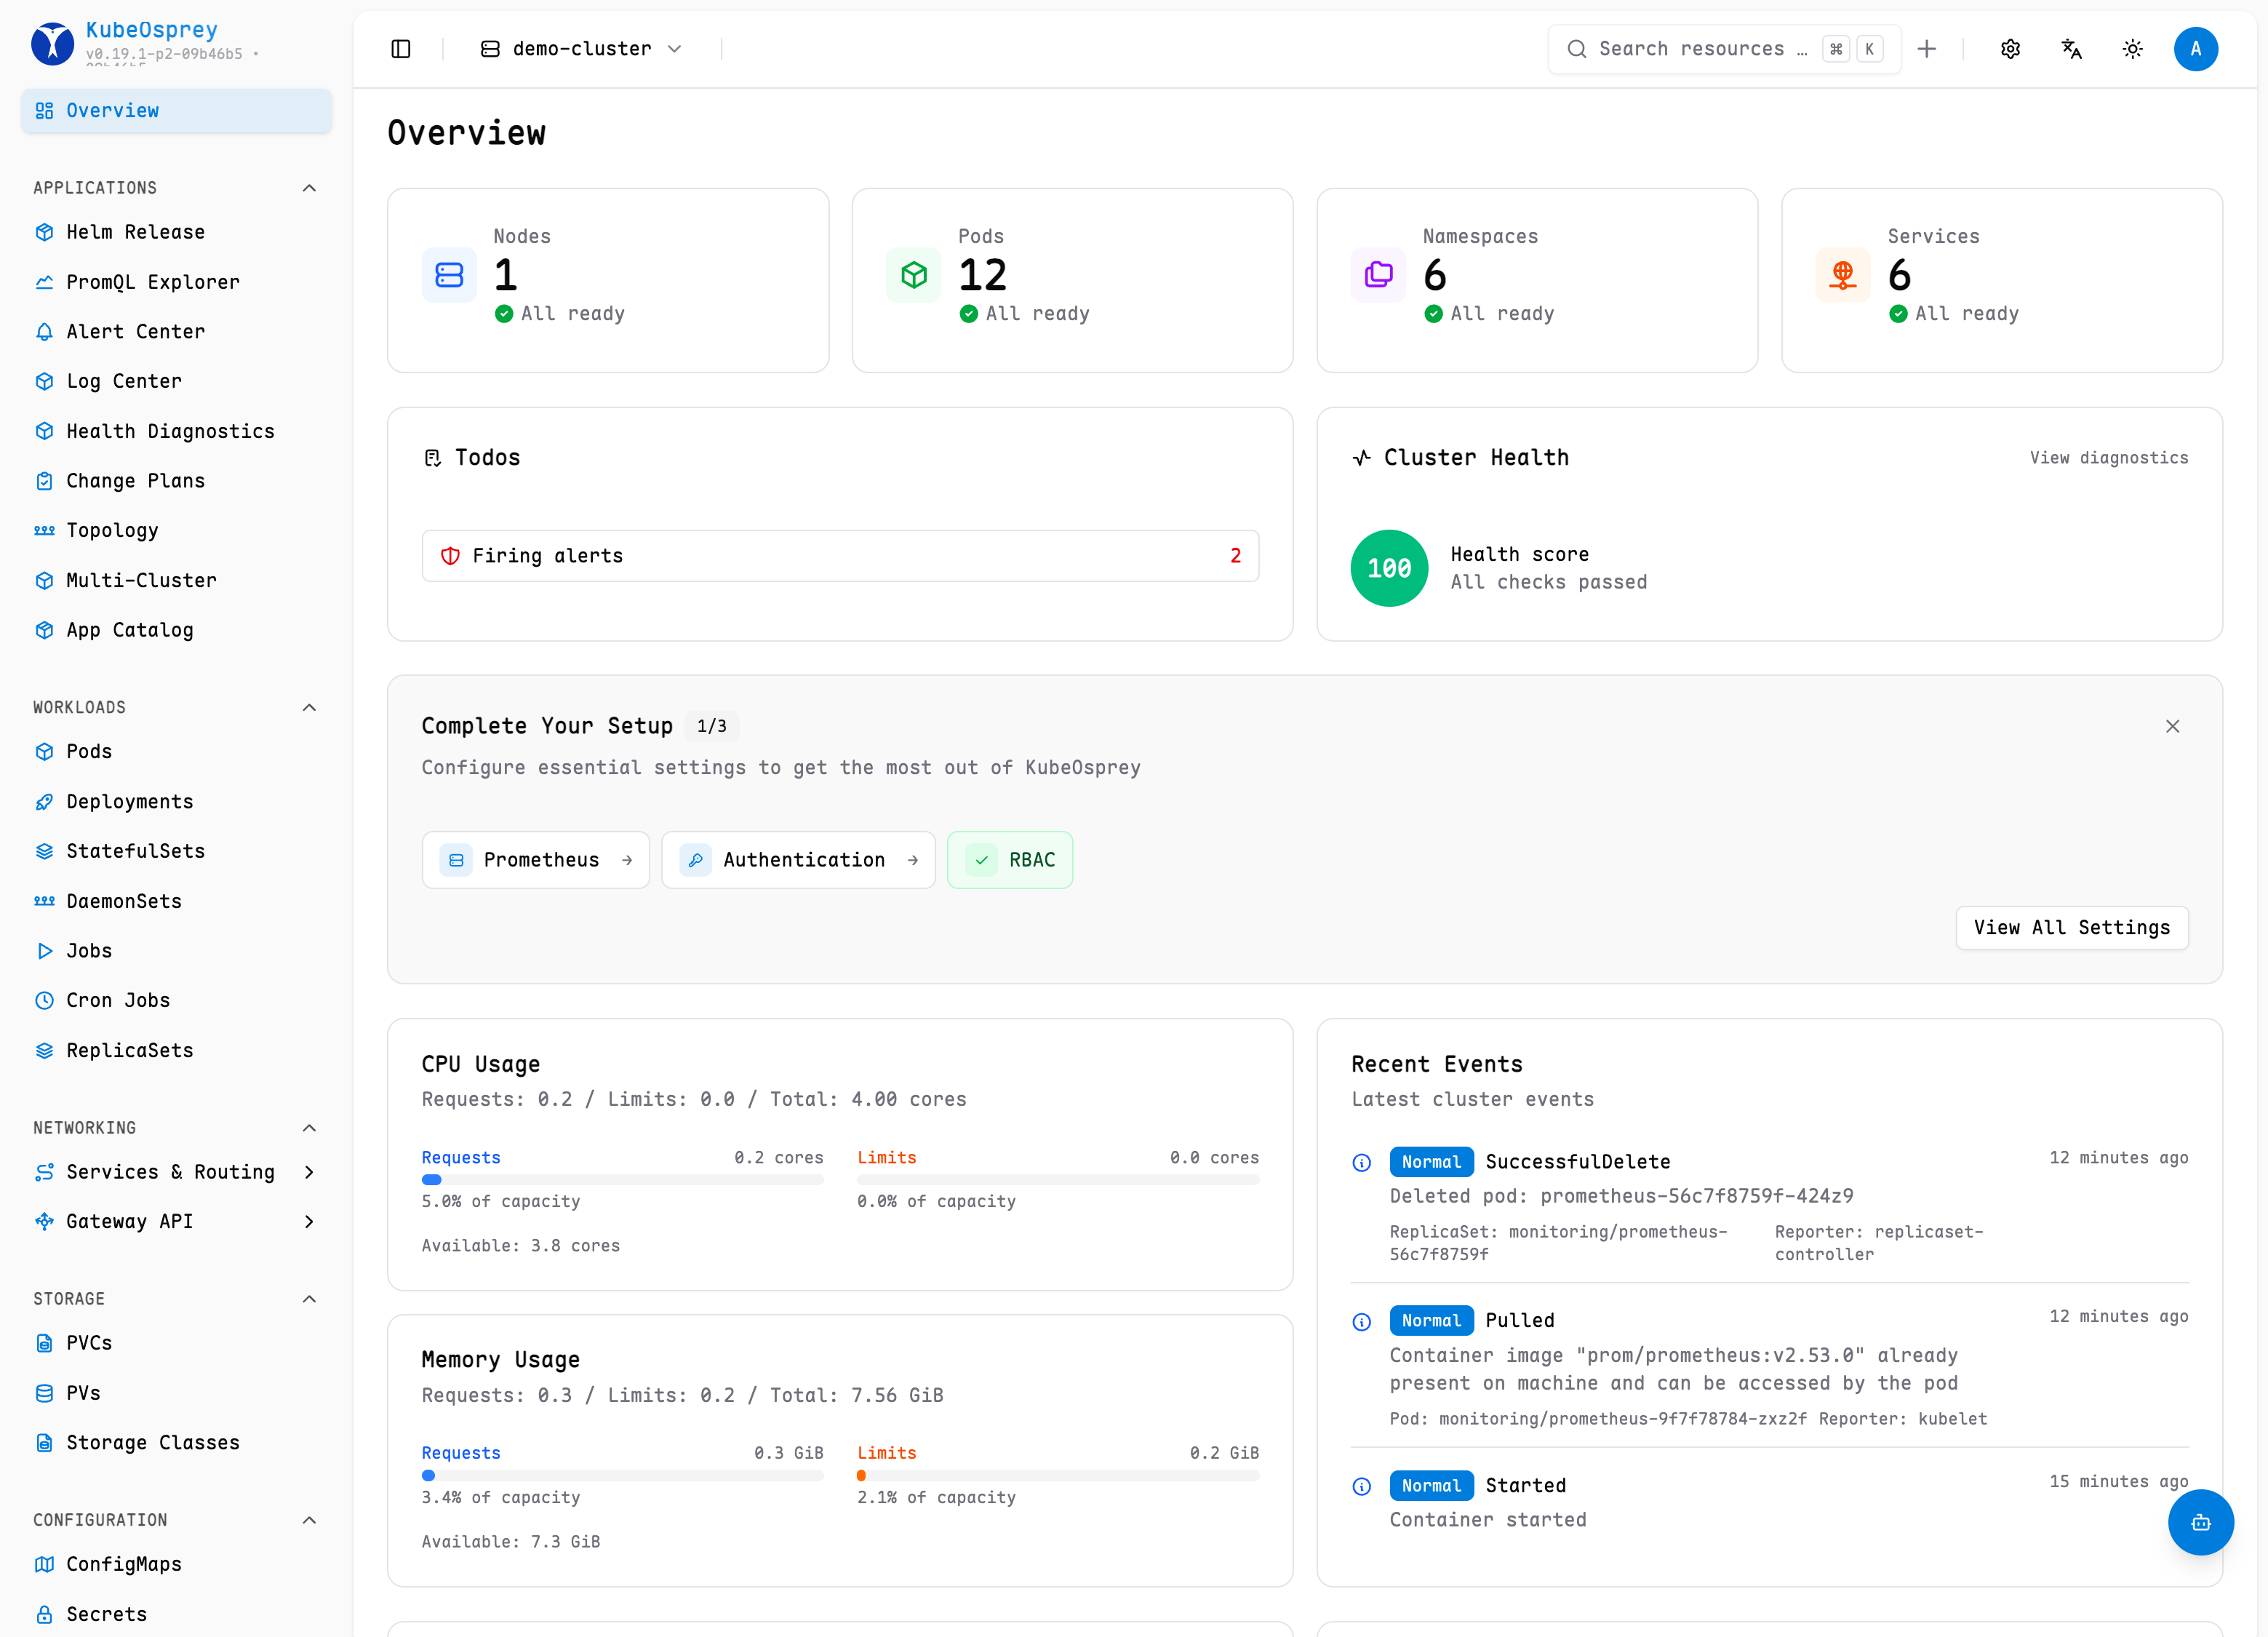
Start here
Fastest evaluation path
Install KubeOsprey with Helm, use port forwarding for the first visit, then connect the in-cluster Kubernetes API. You can complete the initial setup without preparing a kubeconfig.
- Install KubeOsprey and open the dashboard.
- Set up users and RBAC before inviting your team.
- Connect Prometheus when you are ready to add cluster metrics.
Find the right guide
- See how the pieces fit together: Architecture
- Find any resource quickly: Global Search
- Understand a workload and its dependencies: Related Resources
- Investigate a running Pod: Logs and Web Terminal
- Stream logs from many pods at once: Log Center
- Track cluster health and usage: Monitoring
- Triage alerts and silences: Alert Center
- Assess cluster health at a glance: Health Diagnostics
- Edit many workloads at once: Batch Operations
- Install and manage releases: Helm Management
- Gate sensitive changes behind approval: Change Plans
- Review resource changes: Resource History
- Troubleshoot with an AI agent: AI Assistant
- Connect private or remote clusters: KubeOsprey Cluster Agent
Platform at a glance
Observe
Use real-time CPU, memory, and network charts, live Pod logs, events, and resource relationships to move from a symptom to its context. The Log Center aggregates logs across pods, the Alert Center surfaces Alertmanager alerts, and Health Diagnostics scores each cluster's health.
Operate
Create and edit Kubernetes resources, manage Helm releases, open Pod and Node terminals, run kubectl, and access workloads through Kube Proxy. Batch Operations applies image updates, restarts, and scaling to many workloads at once, and Change Plans puts AI and CI-triggered changes behind a human approval gate with rollback support.
Govern
Manage team access with OAuth, MFA, passkeys, users, RBAC, role mappings, and audit logs across multiple clusters. Role assignments support expiry, and password policies with forced password change keep local accounts safe.
Where KubeOsprey fits
Headlamp and Kubernetes Dashboard are strong tools for inspecting and operating individual clusters. KubeOsprey adds a shared workspace for multi-cluster operations, built-in team governance, observability, and AI-assisted workflows.
If you are evaluating KubeOsprey, continue with the installation guide.